BEC does not need malware. It needs urgency, a familiar name, and one person who pays invoices alone. Here is the dual-channel verify habit Canadian SMBs can run this week — plus what to check in Microsoft 365 after a scare.
Business email compromise · SMB · Canada
In short. Business email compromise (BEC) tricks a trusted person into changing where money goes — vendor banking, payroll, or a wire “just this once.” The control that works is boring: verify every payment change on a channel you already trust, not the email thread. Then harden Microsoft 365 so a stolen mailbox cannot silently forward threads for weeks. Amen Security is a Winnipeg cybersecurity and managed IT shop; we operationalize this for Canadian and US SMBs on Microsoft 365 and hybrid stacks.
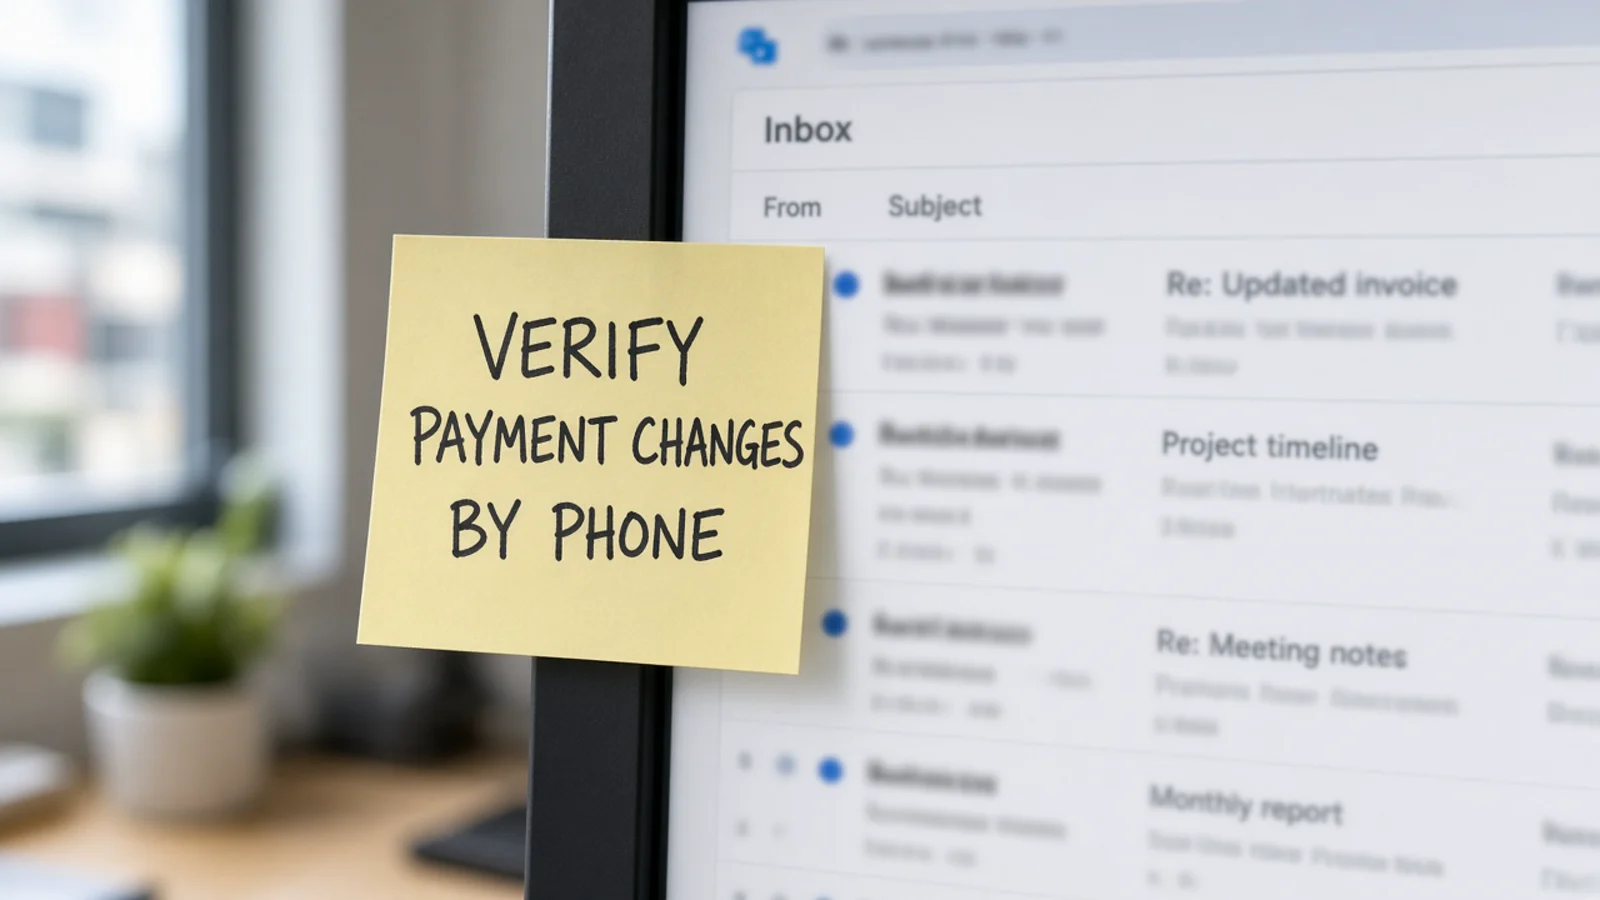
What people actually search. After a near-miss or a news spike, owners and bookkeepers look up business email compromise, BEC scam, and verify vendor payment change. Microsoft, law-enforcement advisories, and CISO blogs all repeat the same sentence: verify out-of-band. This page turns that sentence into a one-page policy your finance desk will follow — then lists the Microsoft 365 checks when a mailbox already looks wrong.
BEC usually starts with a real inbox — yours, a vendor’s, or an executive’s — not a malicious attachment. Attackers read enough mail to mimic tone, timing, and thread history. They wait until someone asks about an invoice, then slip in new banking details or a “updated PDF.” Sometimes they spoof without a compromise; sometimes they live inside the mailbox for days and hide with inbox rules. Either way, the loss is a human clicking Send on a payment that felt routine.
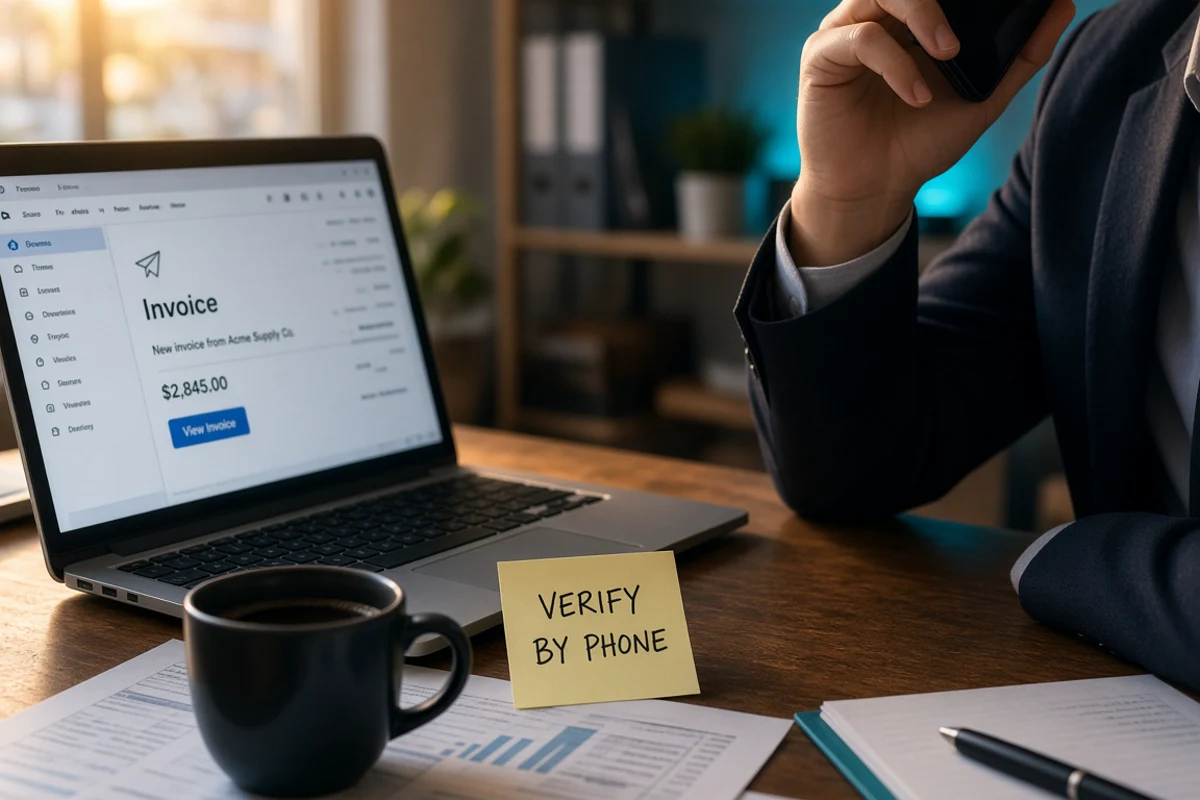
If the message asks you to change where money goes, the message is not enough — even when the thread looks perfect and the signature is theirs.
“Close the books tonight.” Helping feels professional; pausing to call feels like letting the team down. Attackers engineer that guilt on purpose.
They reply inside a real vendor conversation — sometimes from a compromised mailbox you have emailed for years.
No second approver means no friction. Dual control is cheaper than arguing with a bank after a wire is gone.
Training videos about spelling mistakes do not fix this. The mail is often fluent. What fixes it is a written rule everyone hears from the owner: we verify payment changes by phone, using a number that was already on file before the email arrived.
After money moves. Call the bank immediately — recovery windows are short. Preserve headers and logs, but do not wait for perfect forensics to alert the institution. Document the dual-channel steps you attempted; that matters for insurance and law enforcement reports.
Humans first; then identity. Most BEC paths involve password reuse, legacy clients, or mailbox rules attackers add after sign-in. Pair people policy with the controls in our Microsoft 365 MFA guide and tenant hygiene in M365 cleanup.
Run this when someone reports odd sends, a vendor says they never changed banking details, or MFA prompts they did not request.
Read it once at a staff meeting. A policy nobody rehearsed is wallpaper.
Book a BEC and Microsoft 365 payment-controls review
Is BEC only wire fraud? No — EFT changes, payroll redirects, and fraudulent invoices count. Same verify habit.
Do we need a SOC? Most SMBs need MFA, forwarding controls, and a finance ritual — not 24/7 SOC theatre.
What if the vendor’s mailbox was real but hacked? That is classic BEC. Your verify call catches it when their IT has not.
Who is Amen? Winnipeg MSP — email, managed IT, French when tickets are French. Remote across Canada and the US.
Post “We verify every banking change by phone” where AP and payroll see it daily, and kill external mailbox forwarding in Microsoft 365 this week. Request the review
Your comment will be published after our team reviews it.
Keep reading
Unused licences, departed staff accounts, and Microsoft 365 security settings nobody finished turning on: what a cleanup fixes for Canadian SMBs in practice.
A cybersecurity assessment in Canada should define systems, evidence, deliverables and exclusions before work starts. Request a findings register, a prioritized action list and a handover walkthrough; agree implementation separately. It is not automatically a penetration test, certification, insurance approval or ongoing monitoring.