Unused licences, departed staff accounts, and Microsoft 365 security settings nobody finished turning on: what a cleanup fixes for Canadian SMBs in practice.
For most 30–80 seat businesses, a cleanup is the highest-value few hours in their whole Microsoft 365 tenant — and yes, it can be done for you. A cleanup means two things: stop paying for licences that belong to people who left, or for a plan tier whose security tools were never switched on — and finish the security settings that were left half-configured the day the tenant was set up. Neither half requires buying anything new.
In 30 seconds
Is your tenant due? Tick any that sound familiar
One tick is enough — a cleanup starts by finding out which of those situations you are in.
Pull the list of licenced accounts and sort it against who actually works here. Departed employees, duplicate accounts from a name change, and test accounts from old projects are the usual finds. Removing a licence from an account that should not exist is both a saving and a security fix — the two are the same list.
Microsoft describes Business Premium as including all the same apps and services as Business Standard "plus advanced cyberthreat protection and device management capabilities." Microsoft's own Business Premium page lists five security services built into the subscription, not sold as add-ons: Microsoft Defender for Business, Microsoft Defender for Office 365 Plan 1, Microsoft Entra ID Plan 1, Microsoft Intune Plan 1, and Microsoft Purview. Business Standard includes none of those five — its identity tier is the free version of Entra ID, per Microsoft's plan comparison.
Security service | Microsoft 365 Business Standard | Microsoft 365 Business Premium |
|---|---|---|
Microsoft Defender for Business | Not included | Included |
Microsoft Defender for Office 365 Plan 1 | Not included | Included |
Microsoft Entra ID Plan 1 | Not included — Standard's identity tier is the free version of Entra ID | Included |
Microsoft Intune Plan 1 | Not included | Included |
Microsoft Purview | Not included | Included |
Microsoft describes Business Premium as including all the same apps and services as Business Standard "plus advanced cyberthreat protection and device management capabilities." Two boundaries from the same comparison: Microsoft lists Defender for Business standalone at CAD $4.10 per user per month, and notes it is "Included in Microsoft 365 Business Premium"; and Microsoft's business plans are designed for organizations with up to 300 users, with a tenant limit of 300 provisioned licences across the business plan family. Conditional Access — the proper replacement for security defaults — requires at least Entra ID P1, which is the identity tier in the Premium column, not the free tier in the Standard column.
So the tier question cuts both ways. A business on Premium that never turned on Defender for Business or Intune is paying for protection it does not have. A business on Standard that separately bought a standalone endpoint tool may be paying twice — or may be missing Conditional Access entirely, because that requires Entra ID P1. (Microsoft lists Defender for Business standalone at CAD $4.10 per user per month on that page, and notes it is "Included in Microsoft 365 Business Premium.")
One boundary worth knowing: Microsoft's business plans are designed for organizations with up to 300 users, with a tenant limit of 300 provisioned licences across the business plan family. At 30–80 seats you are comfortably inside that — but growth eats it faster than owners expect.
That read-only first look is what our free assessment opens with — the licence list set against the staff list, and nothing changes until you've seen what it finds.
Microsoft's security defaults are a preconfigured baseline: every user registers for multifactor authentication, administrators do MFA, legacy authentication protocols and device code flow are blocked, and privileged activities like reaching the Azure portal are protected. Microsoft's reasoning is blunt — in its words, "more than 99.9% of those common identity-related attacks are stopped by using multifactor authentication and blocking legacy authentication."
The problem is rarely that defaults are bad. It is that nobody knows the tenant's state: defaults on, defaults off with nothing replacing them (the dangerous one), or defaults replaced by Conditional Access policies. Microsoft Learn is explicit that if you disable security defaults, you enable Conditional Access policies immediately to take their place — and Conditional Access requires at least Microsoft Entra ID P1, which is the licence tier question from the first half, coming back around.
"I think MFA is on" is the most common answer we hear, and it is a guess, not a setting.
Two quieter items finish the settings pass. First, admin roles: how many accounts hold Global Administrator, whether they are separate accounts used only for admin work, and whether the emergency ("break-glass") accounts Microsoft recommends — two cloud-only accounts, permanently assigned the Global Administrator role — exist and are documented. Second, app consent: which third-party apps your users have granted access to your tenant, and whether ordinary users can keep granting more. (What that consent can be turned into, an attacker demonstrated in October 2026 — our Microsoft 365 backup security checklist walks through reviewing connected apps after that incident.)
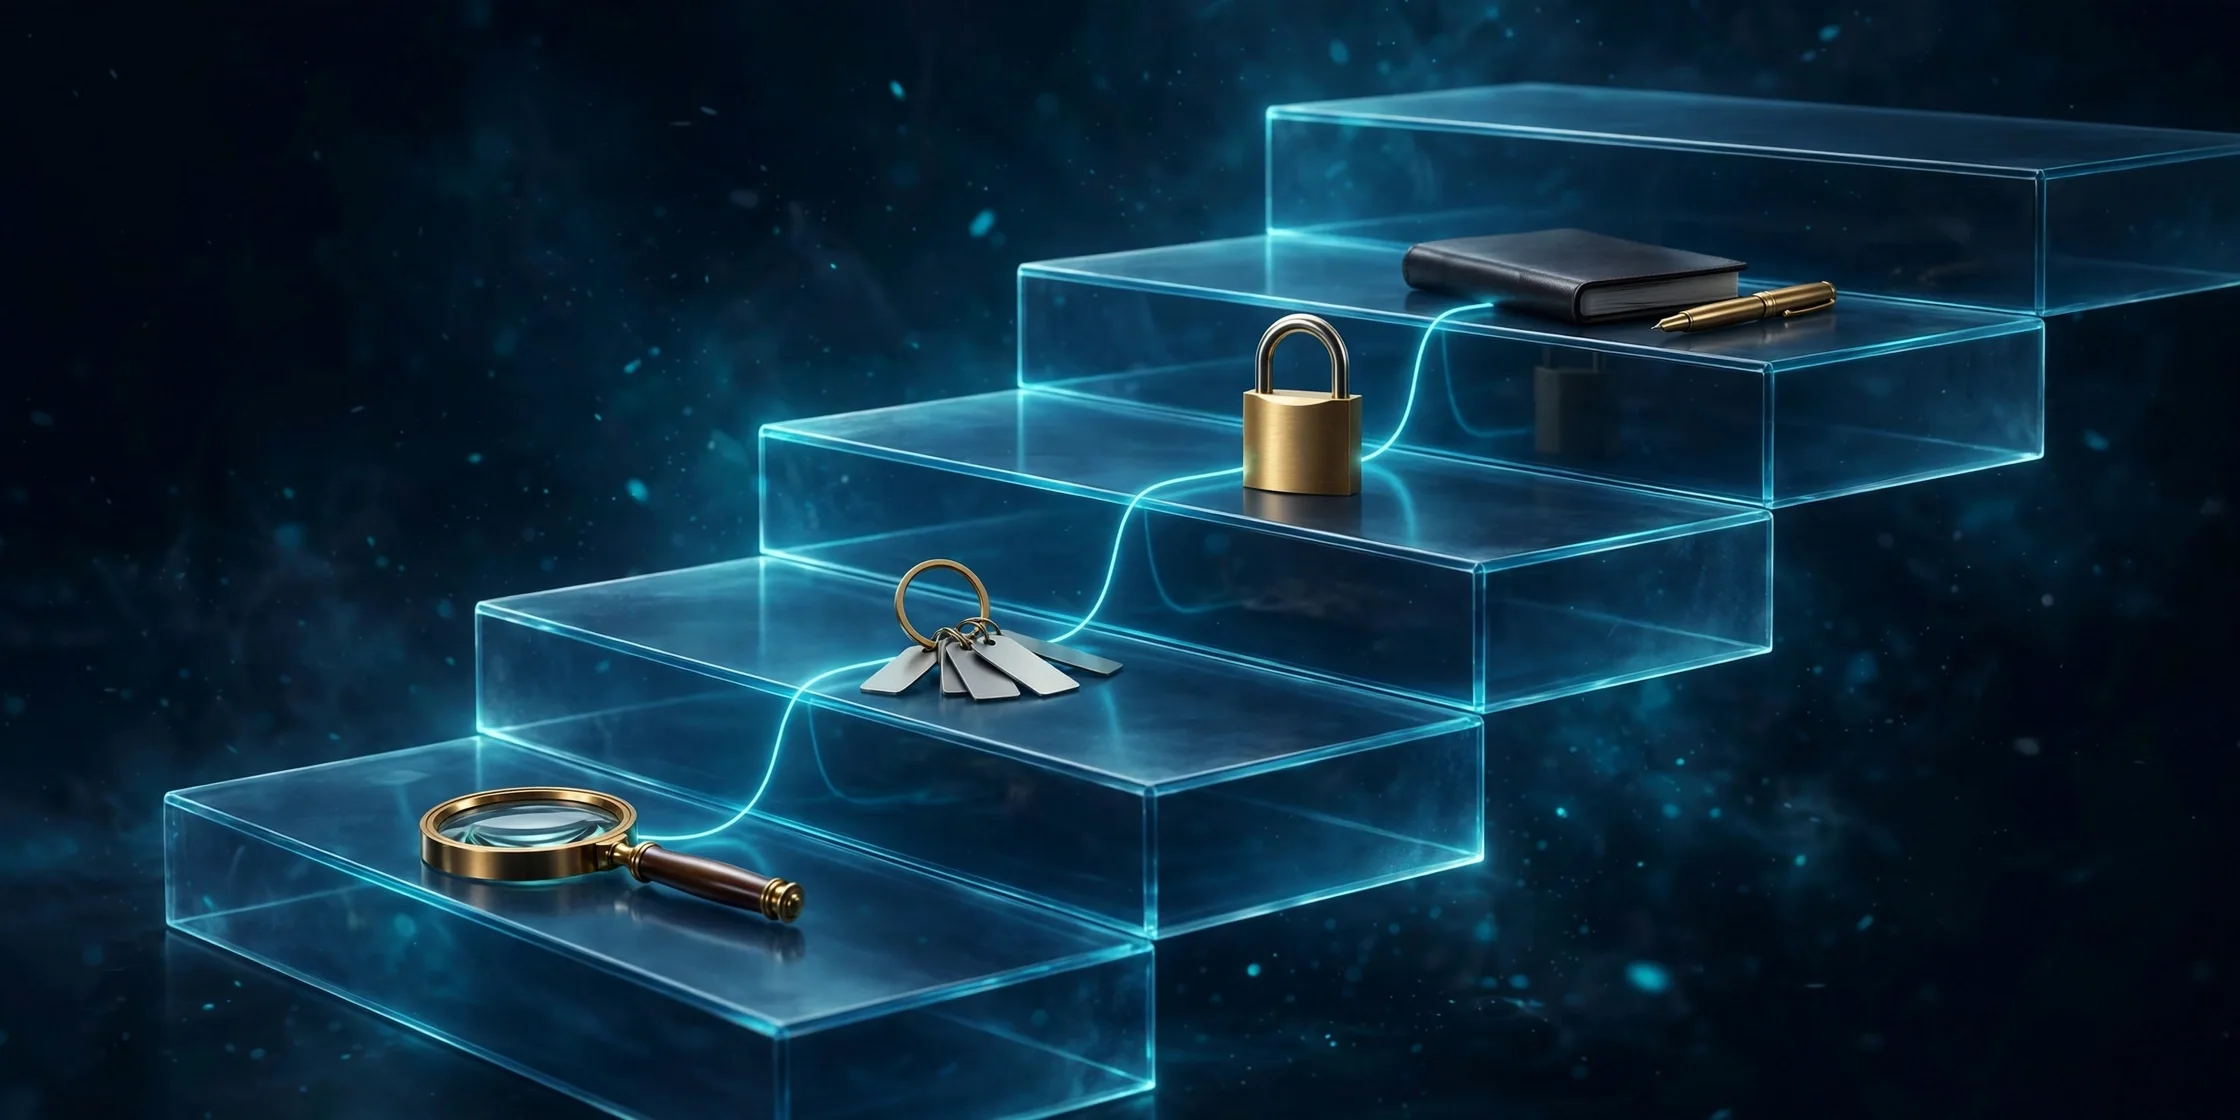
The cleanup, in order: Audit → Licence fixes → Settings fixes → Written record.
Amen's part in this can sit in either of our lanes, depending on what the audit finds: it is tenant work under our Server & Cloud services, and the email side of it — filtering, authentication records, the accounts attackers actually aim at — sits under Email & Communication.
Why are we paying for Microsoft 365 licences nobody uses?
Because licences are assigned to accounts, not people, and accounts outlive roles. Someone leaves, a mailbox gets converted but keeps its licence, a project account never gets closed. The fix is rhythm, not a purge: reconcile the licence list against the staff list every quarter, and make licence removal part of offboarding — which is also when the account stops being a security risk.
What Microsoft 365 settings should be turned on for security by default?
Start with Microsoft's own baseline: security defaults enabled (or properly replaced by Conditional Access), which means every user registered for MFA, administrators doing MFA, legacy authentication and device code flow blocked, and privileged activities protected. Then the items defaults don't cover for you: a reviewed admin-role list, break-glass accounts, and user consent to third-party apps restricted. Microsoft Secure Score, in the admin center, shows where your tenant stands against Microsoft's recommendations.
How much does a Microsoft 365 migration cost for a 40-person company?
A migration — moving mail and files into Microsoft 365 from somewhere else — is priced by what is being moved: mailboxes, where the files live today, data volume, and how much cleanup the source needs on the way in. It is a different job from a cleanup, which works on a tenant you already have; our cloud migration checklist covers how a move is staged. Amen quotes migrations after an assessment rather than publishing a per-seat number, because the source environment changes the work more than the seat count does.
Who does Microsoft 365 setup and support for businesses in Winnipeg?
Amen Security does — setup, tenant cleanup, and ongoing support for Winnipeg businesses, with on-site work across Manitoba and remote delivery across Canada and the US. It sits inside our managed and cloud services rather than as a one-off product, which matters for a cleanup: the point is that someone keeps the tenant from drifting back.
A cleanup doesn't live alone in a tenant. It has two neighbours, and most businesses end up doing all three within a year of each other:
Most tenants do not need a bigger plan or a new tool — and most cleanups, done once, quietly un-happen. Licences creep back on for people who've left. A new app gets consented to on a busy Friday. The defaults get changed for one urgent fix and never changed back. Drift isn't a failure of the first cleanup; it's what a tenant does when nobody's watching.
So make the second cleanup boring. Once a quarter, put the licence list beside the staff list: who joined, who left, whose role changed enough to change their tier. Tie licence removal to offboarding, so the account closes the same week the desk does. Keep the short written record from the first pass updated — your defaults state, your admin list, your approved apps — because that record is the difference between an hour of housekeeping and another dig.
The first cleanup is excavation. Every one after it should be a broom, not a shovel.
Sources & review
Your comment will be published after our team reviews it.
Keep reading
A backup app's stolen credential opened Microsoft 365 tenants in October 2026. This Canadian SMB checklist audits app access, permissions and restores.
A practical order of operations for moving workloads to Microsoft 365 and Azure: inventory, identity, networking, data residency, and rollback — without the weekend surprise.